Retrieval / search
Chemister
Search and question answering over 200,000+ chemistry papers.
- Problem
- Chemistry papers are hard to search by meaning. Keyword search misses papers that describe the same reaction in different words, and there is no simple way to search by molecule structure.
- What I built
- An ingestion pipeline, bge-m3 embeddings, a FAISS vector index, hybrid keyword and vector ranking, and a FastAPI service. Answers cite the papers they come from. A molecule editor lets you search by structure.
- Result
- One service that searches the whole corpus in seconds and returns cited answers. Code is private; a walkthrough is available on request.
Application platform
Lumen
A home server that builds and serves apps to a thin phone client.
- Problem
- Phone apps are slow to change. I wanted to describe a small tool and have it on my phone the same day, without an app store release.
- What I built
- An async FastAPI hub that serves apps to a minimal Android WebView shell, with WebSocket push, WebAuthn login, versioned file writes, and an LLM-assisted build step that writes new apps.
- Result
- 33 apps served from one hub. New apps and fixes reach the phone during a session with no reinstall.
AI security testing
LLM Attack Catalogue
31 documented ways to attack an LLM application, written so software can plan tests from them.
- Problem
- Prompt-injection advice is usually a list of example prompts. That does not tell a tester when an attack applies, or what it proves when it works.
- What I built
- A catalogue of 31 techniques. Each one is mapped to OWASP Top 10 for LLM Applications and MITRE ATLAS, has a write-up, and states its preconditions and results in a format an automated test planner can read.
- Result
- Coverage from direct and indirect injection through agent memory poisoning and model output reaching SQL, shell, and SSRF sinks. A small probe suite runs the basic cases against any chat endpoint.
Human-approved security testing
BS2
An AI-assisted testing engine where every action on a target needs an exact human approval.
- Problem
- AI agents that run security tools can act outside their scope, and their reports can claim things the evidence does not show.
- What I built
- The model proposes; a separate gate executes. Every request needs an approval tied to the exact command, destination, and policy, and it expires. Scope is rechecked before each action. Unsupported commands are refused.
- Result
- Open source. The 0.2.1 release passes 271 regression tests, and findings come from what actually happened, never from the model's confidence.
Security monitoring
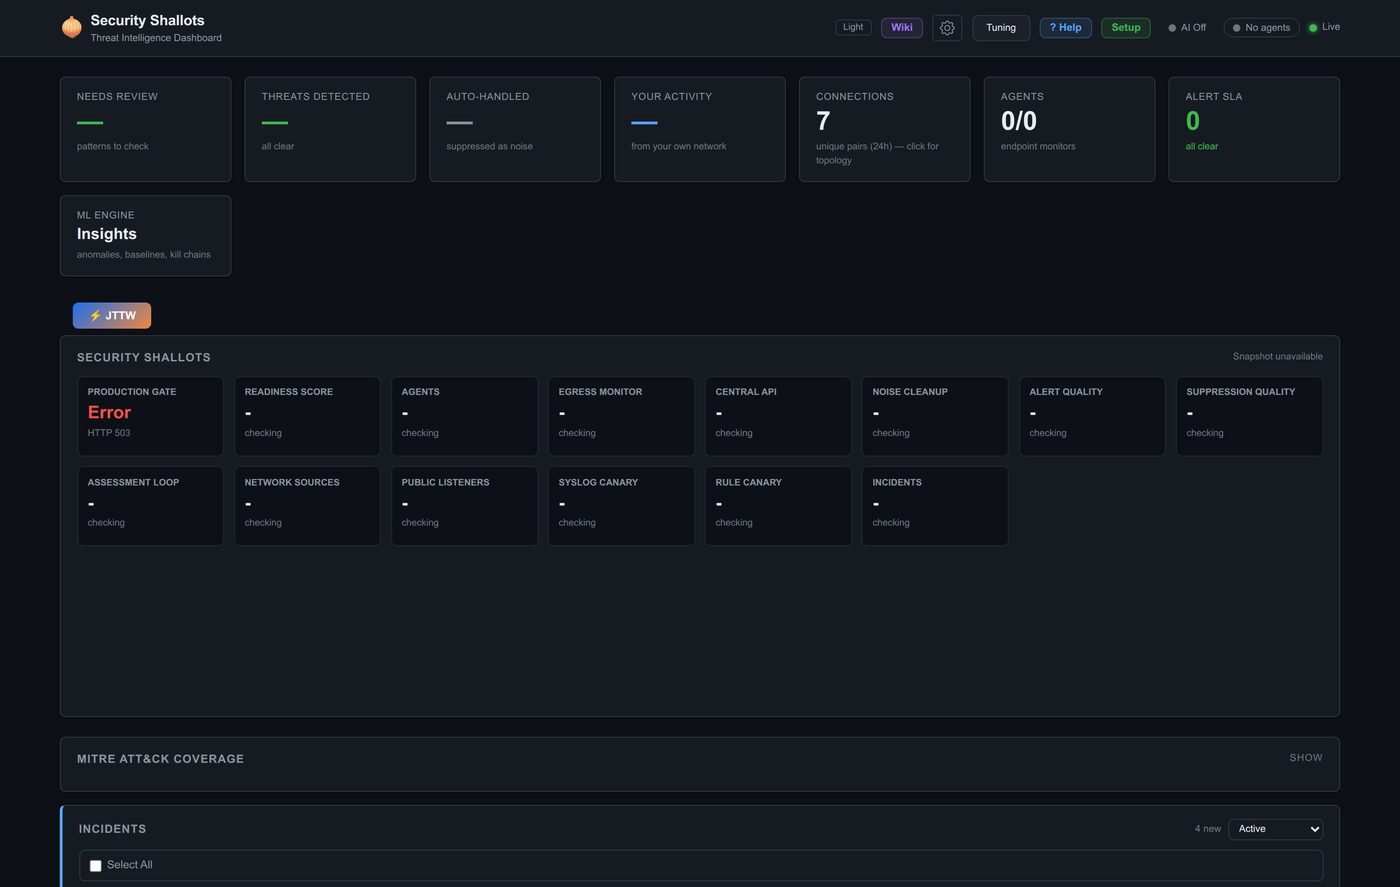
Security Shallots
Security monitoring for a home lab or small office, on one small box.
- Problem
- Small networks get the same attacks as big ones but cannot run a full SIEM stack or staff a security team.
- What I built
- Collection of network, host, and router signals, threat-intelligence lookups, cross-event correlation, and a local language model that turns alert clusters into plain-English incidents with a runbook.
- Result
- Known noise is suppressed automatically, the rest is ranked, and every finding keeps its source evidence. Runs on a Raspberry Pi class machine.